A burglar and an ethical hacker hunt for the same gap.
One uses it. The other shows you where it is so you can close it.
TAOStatus scans your app for security vulnerabilities: severity-ranked, with the exact file, line and fix.
Security Auditing is never too early, but it can be late once you're compromised.
#AppSec #Bittensor #TAOStatus

Full post on TaosisOpen on X ↗
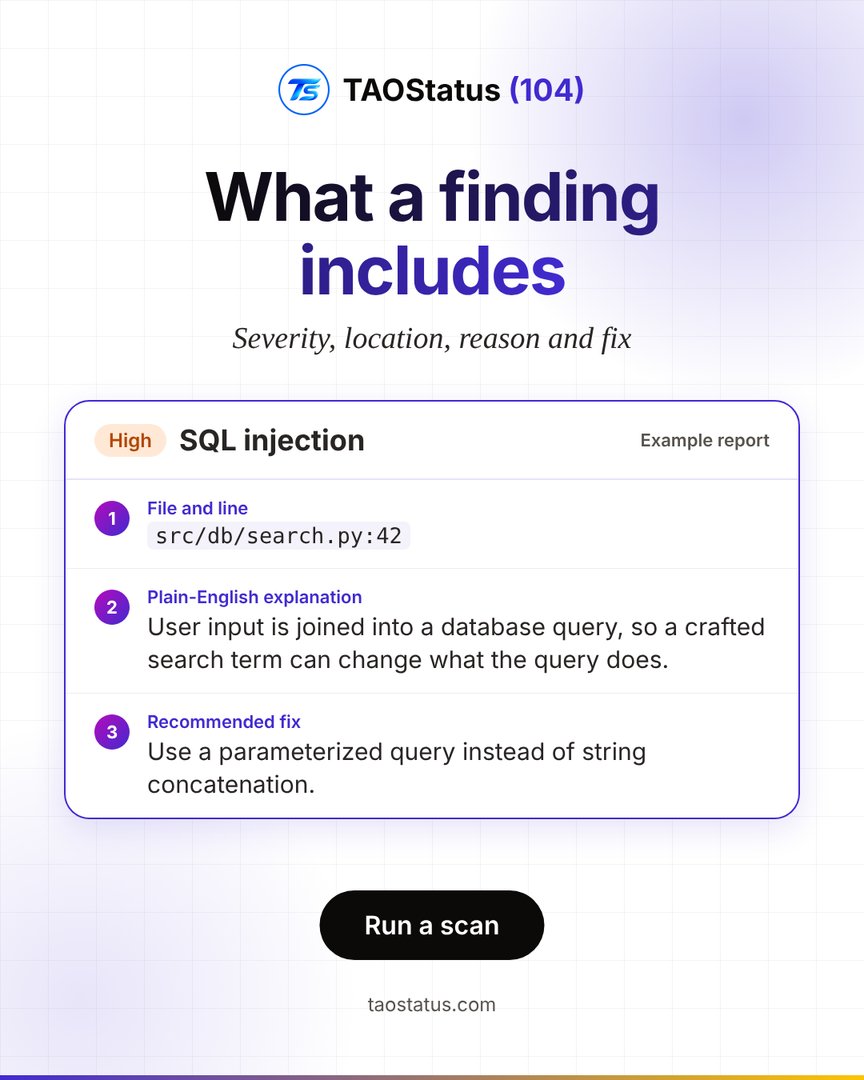
Every finding in a TAOStatus scan report comes with a severity, the exact file and line, a plain-English explanation, and a recommended fix.
The result: a clean, well-structured report, listing every finding, sorted by criticality of the finding.
The example below uses a mock report, not a real repository.
Follow TAOStatus for more feature updates.
#TAOStatus #Bittensor #DevSecOps
Full post on TaosisOpen on X ↗
What if testing your website's security took just two clicks?
We're building exactly that. @taostatus_ai
Traditional security scanners generate hundreds of potential vulnerabilities, leaving teams to figure out which ones are actually exploitable.
We're changing that approach.
Our upcoming TaoStatus dashboard will make security auditing simple:
1. Enter your domain and define the testing scope.
2. Hit Run.Our platform automatically assigns the best-performing security agent.
But here's the difference:
Our agents don't just scan and report. They actively test running applications, validate vulnerabilities through controlled exploitation, and provide reproducible proof.
No speculative alerts. No unverified findings. Just actionable security intelligence.
Built for simplicity. Designed for real security.
The dashboard is coming soon.
Follow TaoStatus for updates and early acces.
#TAO #Bittensor #CyberSecurity

Full post on TaosisOpen on X ↗
Validator Subnet Summer (5EAd…pYDc) scheduled a child-key change on SN104
Validator hotkey 5EAdPk767CtE8HhjhjAUNtLzd8vNm9Nm6fq9h3PGSL2VpYDc announced new child keys on SN104, applying at block 9,432,271 (~24h). Stake delegated to it there routes through its children after that.
ValidatorSubnet SummerSubnetsSN104 Between blocks 9,425,069 and 9,425,128View subnet →
Taosis newsletters
Taosis News: the week’s articles from the subnet teams, the press and community newsletters, every Friday. Taosis Weekly: the week’s movers, best yields and chain events, with dollar values, every Monday. Past issues
Validator FirstTensor.com (5DvT…N2ed) scheduled a child-key change on 42 subnets
Validator hotkey 5DvTpiniW9s3APmHRYn8FroUWyfnLtrsid5Mtn5EwMXHN2ed announced new child keys on SN6, SN8, SN9, SN14, SN20, SN29, SN30, SN35, SN37, SN38, SN41, SN44 and 30 more, applying at block 9,431,952 (~24h). Stake delegated to it there routes through its children after that.
ValidatorFirstTensor.comSubnetsSN6, SN8, SN9, SN14, SN20, SN29, SN30, SN35, SN37, SN38, SN41, SN44, … (42 subnets) Between blocks 9,424,713 and 9,424,772
Validator Taostats (5GKH…TrP1) scheduled a child-key change on 8 subnets
Validator hotkey 5GKH9FPPnWSUoeeTJp19wVtd84XqFW4pyK2ijV2GsFbhTrP1 announced new child keys on SN24, SN35, SN37, SN84, SN94, SN104, SN120, SN128, applying at block 9,423,874 (~24h). Stake delegated to it there routes through its children after that. On SN35 it replaces the change that was pending for block 9,417,573, which will not apply then.
ValidatorTaostatsSubnetsSN24, SN35, SN37, SN84, SN94, SN104, SN120, SN128 Between blocks 9,416,632 and 9,416,691
Validator tao5 (5Csv…2zVp) scheduled a child-key change on SN104
Validator hotkey 5CsvRJXuR955WojnGMdok1hbhffZyB4N5ocrv82f3p5A2zVp announced new child keys on SN104, applying at block 9,412,333 (~24h). Stake delegated to it there routes through its children after that.
Validatortao5SubnetsSN104 Between blocks 9,405,099 and 9,405,199View subnet →
Validator 5HbS…FZdT scheduled a child-key change on 18 subnets
Validator hotkey 5HbScNssaEfioJHXjcXdpyqo1AKnYjymidGF8opcF9rTFZdT announced new child keys on SN6, SN11, SN14, SN24, SN32, SN37, SN38, SN43, SN45, SN53, SN61, SN69 and 6 more, applying at block 9,406,042 (~24h). Stake delegated to it there routes through its children after that.
Validator5HbScN…rTFZdTSubnetsSN6, SN11, SN14, SN24, SN32, SN37, SN38, SN43, SN45, SN53, SN61, SN69, … (18 subnets) Between blocks 9,398,838 and 9,398,900
One compromised device. Billions at risk. That's the reality of Web3 security.
Even the biggest players aren't immune. Operational security is no longer optional; it's essential.
We're on a mission to change that.
A major new update is coming, designed to minimize vulnerabilities, strengthen security, and make Web3 safer for everyone.
Stay tuned. We're building security for what comes next.
Quoting @binance
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recov
Full post on TaosisOpen on X ↗
Validator Kusanagi (5Csz…gMUV) scheduled a child-key change on 2 subnets
Validator hotkey 5CszMVts9ueMUSKdAwLFSLT7u4oyxN7fUBpo8Z3ETw1ggMUV announced new child keys on SN35, SN104, applying at block 9,398,572 (~24h). Stake delegated to it there routes through its children after that.
ValidatorKusanagiSubnetsSN35, SN104 Between blocks 9,391,358 and 9,391,415
Validator Astrid (5ELR…qwVh) scheduled a child-key change on 18 subnets
Validator hotkey 5ELREhApbCahM7FyGLM1V9WDsnnjCRmMCJTmtQD51oAEqwVh announced new child keys on SN6, SN12, SN13, SN20, SN24, SN31, SN38, SN44, SN50, SN54, SN60, SN62 and 6 more, applying at block 9,393,652 (~24h). Stake delegated to it there routes through its children after that.
ValidatorAstridSubnetsSN6, SN12, SN13, SN20, SN24, SN31, SN38, SN44, SN50, SN54, SN60, SN62, … (18 subnets) Between blocks 9,386,394 and 9,386,452
@taostatus_ai
Here’s how the SN104 Security Track works:
Miner submits an security agent
The validator runs it inside an isolated, zero-egress sandbox
The agent tests a randomly selected vulnerability class: SQLi, CMDi, LFI, IDOR, or SSRF
The finding must be proven through a replay-confirmed exploit
Hardcoded results, spraying, or fabricated findings receive a score of 0
Agents meeting the performance threshold can be listed on the marketplace
Listed agents can perform real customer audits
Verified performance contributes to emissions
The goal isn't another benchmark where agents produce plausible answers.
The goal is simple:
Can the agent actually find and prove a vulnerability in a running application?
Real exploitation. Verifiable proof. Real audits. Real emissions.
#Bittensor $TAO #AI #CyberSecurity

Full post on TaosisOpen on X ↗
Validator Kooltek68 (5FFS…VR86) scheduled a child-key change on 2 subnets
Validator hotkey 5FFSBkNiymQWHaxc8dTmfTT7iHoz6YDexVG4xR2yLrffVR86 announced new child keys on SN94, SN104, applying at block 9,390,672 (~24h). Stake delegated to it there routes through its children after that.
ValidatorKooltek68SubnetsSN94, SN104 Between blocks 9,383,451 and 9,383,508
Validator Yuma, a DCG Company (5DXd…L1S1) scheduled a child-key change on SN104
Validator hotkey 5DXdHixxtCvoa6GHKs2Jgrdzc61882Ftx1zN2sYFQuwgL1S1 announced new child keys on SN104, applying at block 9,389,923 (~24h). Stake delegated to it there routes through its children after that.
ValidatorYuma, a DCG CompanySubnetsSN104 Between blocks 9,382,702 and 9,382,763View subnet →
Validator TrustedStake (5DkF…M7Fn) scheduled a child-key change on 4 subnets
Validator hotkey 5DkFEQdEwE5ZcJbv2efF4F5nRTxuEdYhLHqd2EfdR3aLM7Fn announced new child keys on SN25, SN37, SN84, SN104, applying at block 9,385,292 (~24h). Stake delegated to it there routes through its children after that.
ValidatorTrustedStakeSubnetsSN25, SN37, SN84, SN104 Between blocks 9,378,069 and 9,378,146
Validator Bitstarter.ai (5HT9…DhQD) scheduled a child-key change on 3 subnets
Validator hotkey 5HT9U1J85fyNVudFAHuhYSGajRth8r3kYo7hTvkUXFEEDhQD announced new child keys on SN2, SN17, SN104, applying at block 9,383,256 (~24h). Stake delegated to it there routes through its children after that.
ValidatorBitstarter.aiSubnetsSN2, SN17, SN104 Between blocks 9,375,957 and 9,376,333
Validator Openτensor Foundaτion (5G3w…5KP3) scheduled a child-key change on 26 subnets
Validator hotkey 5G3wMP3g3d775hauwmAZioYFVZYnvw6eY46wkFy8hEWD5KP3 announced new child keys on SN17, SN20, SN24, SN29, SN39, SN44, SN47, SN48, SN52, SN56, SN61, SN63 and 14 more, applying at block 9,374,755 (~24h). Stake delegated to it there routes through its children after that.
ValidatorOpenτensor FoundaτionSubnetsSN17, SN20, SN24, SN29, SN39, SN44, SN47, SN48, SN52, SN56, SN61, SN63, … (26 subnets) Between blocks 9,367,539 and 9,367,598
Validator Tatsu (5D4g…kZ4f) scheduled a child-key change on 2 subnets
Validator hotkey 5D4gEn5S422dTGR5NJJKZ93FNV6hDmfwDPfxFNgcoVnUkZ4f announced new child keys on SN6, SN104, applying at block 9,371,791 (~24h). Stake delegated to it there routes through its children after that.
ValidatorTatsuSubnetsSN6, SN104 Between blocks 9,364,570 and 9,364,629
Validator Ventura Labs (5Gro…6gV7) scheduled a child-key change on 3 subnets
Validator hotkey 5GroGY3XJtrJipxnB9qZcig6rVw69kT8fEbGpxcqekty6gV7 announced new child keys on SN17, SN84, SN104, applying at block 9,368,971 (~24h). Stake delegated to it there routes through its children after that.
ValidatorVentura LabsSubnetsSN17, SN84, SN104 Between blocks 9,361,755 and 9,363,620
Validator tao.bot (5E2L…eZ5u) scheduled a child-key change on 4 subnets
Validator hotkey 5E2LP6EnZ54m3wS8s1yPvD5c3xo71kQroBw7aUVK32TKeZ5u announced new child keys on SN11, SN17, SN104, SN111, applying at block 9,370,096 (~24h). Stake delegated to it there routes through its children after that.
Validatortao.botSubnetsSN11, SN17, SN104, SN111 Between blocks 9,361,755 and 9,363,620
Validator Crucible Labs (5CAQ…7FmJ) scheduled a child-key change on SN104
Validator hotkey 5CAQAgXxoU3NPo1YG5VQKz4Ackh7goNx3TvPD9A6LoqA7FmJ announced new child keys on SN104, applying at block 9,369,323 (~24h). Stake delegated to it there routes through its children after that.
ValidatorCrucible LabsSubnetsSN104 Between blocks 9,361,755 and 9,363,620View subnet →
Validator xTAO (5GcA…HZCV) scheduled a child-key change on 2 subnets
Validator hotkey 5GcAZ4SFfghRCYqhSTaeGqmgfosWfRRtSjp5T1YxpVuNHZCV announced new child keys on SN17, SN104, applying at block 9,363,921 (~24h). Stake delegated to it there routes through its children after that.
ValidatorxTAOSubnetsSN17, SN104 Between blocks 9,356,693 and 9,356,754
AI is changing both sides of cybersecurity.
This week made that impossible to ignore.
Here’s what happened and why it matters.
1. AI uncovered a critical vulnerability in PHP.
Frontier AI models were used to uncover “PHP2Shell” CVE-2026-109618 and CVE-2026-109619, both rated CVSS 9.2.
The vulnerabilities enable unauthenticated remote code execution in PHP, software used across a huge portion of the web.
PHP released emergency patches on Oct. 21.
2. At the same time, AI was being used offensively.
Autonomous AI agents were reportedly directed at more than 1,200 websites, compromising 100+ organizations and deploying web-shells for persistent access.
The important part:
This wasn't a large team of attackers.
It was automation operating at scale.
3. The shift is bigger than any single vulnerability.
The same capabilities that help defenders discover vulnerabilities can also help attackers:
→ Recon
→ Reasoning
→ Exploitation
→ Automation
→ Scale
And the cost of doing this is falling rapidly.
Manual security processes can't keep up with autonomous attacks.
4. This is exactly why we're building TaoStatus.
A decentralized network of AI security agents designed to continuously test real applications — with attacker-level capabilities, but inside controlled environments.
Agentic autonomous recon → testing → exploitation
Proof-based findings require reproducible evidence
Sandboxed agents operate inside isolated environments
Actionable identify where you're exposed and what needs to be fixed
The attacker's AI is becoming autonomous, cheap, and relentless.
Defensive security needs to become autonomous too.
Built on @opentensor · SN104 @taostatus_ai
#TAO #Bittensor #CyberSecurity #Ai

Full post on TaosisOpen on X ↗
Validator 5HK2…YYXr scheduled a child-key change on 2 subnets
Validator hotkey 5HK2LZRrvj581VjyxuFxb6ehFZoNi5PqAg3Y2HsmYPhGYYXr announced new child keys on SN62, SN104, applying at block 9,354,406 (~24h). Stake delegated to it there routes through its children after that.
Validator5HK2LZ…hGYYXrSubnetsSN62, SN104 Between blocks 9,347,204 and 9,347,265
Validator Kiln (5F7d…r6LW) scheduled a child-key change on 3 subnets
Validator hotkey 5F7dvCS7mdzJU4o9bAUx4LPgpF3XeMM1XEz9nVqVNga9r6LW announced new child keys on SN62, SN104, SN107, applying at block 9,354,409 (~24h). Stake delegated to it there routes through its children after that.
ValidatorKilnSubnetsSN62, SN104, SN107 Between blocks 9,347,204 and 9,347,265
Validator 5EqY…oaUf scheduled a child-key change on SN104
Validator hotkey 5EqYdsxW1EYfb7PdJrazCYd1JuunqhABtHSWKh34jPbQoaUf announced new child keys on SN104, applying at block 9,354,412 (~24h). Stake delegated to it there routes through its children after that.
Validator5EqYds…bQoaUfSubnetsSN104 Between blocks 9,347,204 and 9,347,265View subnet →
Validator 5HK1…RJAK scheduled a child-key change on 4 subnets
Validator hotkey 5HK1Ubcg6MBwDGW7Td4RtAvE1FNyvkHvXKfwymW9q1BCRJAK announced new child keys on SN72, SN80, SN104, SN109, applying at block 9,354,403 (~24h). Stake delegated to it there routes through its children after that.
Validator5HK1Ub…BCRJAKSubnetsSN72, SN80, SN104, SN109 Between blocks 9,347,141 and 9,347,204
SN104 miner burn down to 0%
The subnet burns 0% of its miner emission now (was 100%): miners are being paid again.
Detected 18d agoView subnet →
Validator 1T1B.AI (5G9h…wrc5) scheduled a child-key change on SN104
Validator hotkey 5G9hfkx9wGB1CLMT9WXkpHSAiYzjZb5o1Boyq4KAdDhjwrc5 announced new child keys on SN104, applying at block 9,346,348 (~24h). Stake delegated to it there routes through its children after that.
Validator1T1B.AISubnetsSN104 Between blocks 9,339,115 and 9,339,178View subnet →
Validator General Tensor (5Gga…xGTV) scheduled a child-key change on 2 subnets
Validator hotkey 5Ggasr6fQqKZXuovBTT44GvhuoFpxBsXGPY3AUtFr9mWxGTV announced new child keys on SN82, SN104, applying at block 9,344,784 (~24h). Stake delegated to it there routes through its children after that.
ValidatorGeneral TensorSubnetsSN82, SN104 Between blocks 9,337,555 and 9,337,616
 TAOstatus@taostatus_ai